Live
Aurhanticator
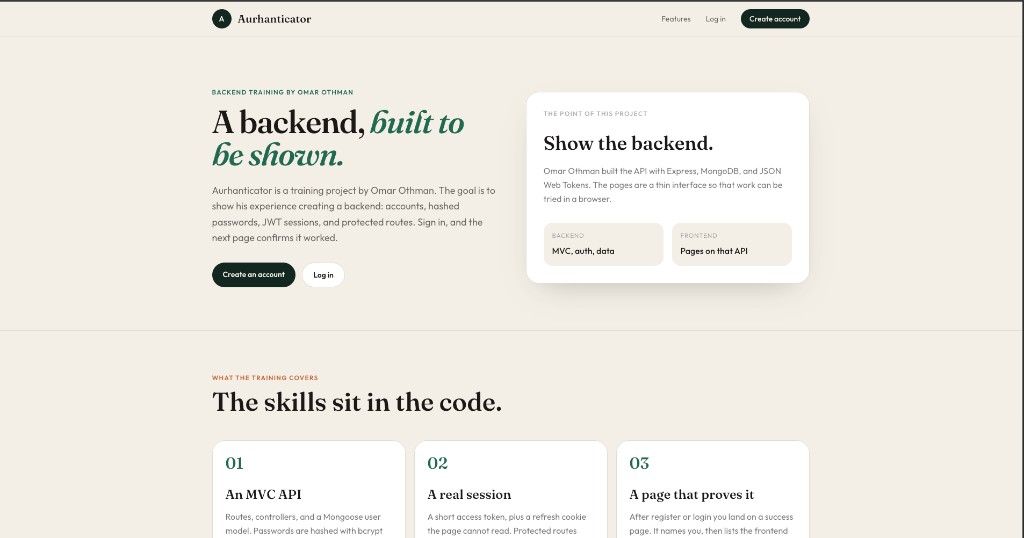
A training project that shows an authentication API. Accounts, hashed passwords, JWT sessions, and protected routes. The pages are a thin front so the API can be tried in a browser.
- Node.js
- Express
- MongoDB
- JWT
- bcrypt
/ Problem
A client that can read document.cookie should not be able to steal a long-lived refresh token. The API had to separate a short-lived access token from a refresh token the page script cannot read.
/ My role
I built the API in an MVC layout with Express and MongoDB, then put a few pages in front of it so a sign-in can be checked in the browser.
/ What I built
- 01Routes, controllers, and a Mongoose user model.
- 02Passwords hashed with bcrypt before they are stored.
- 03A short JWT access token, and a refresh cookie the page cannot read.
- 04Protected routes that check the access token first.
- 05A success page after register or login, so the session can be confirmed.
Refresh-token rotation, rate limiting, and automated tests are not part of what this demo shows.
/ One hard part
Two tokens, two jobs
The access token is what a request presents. The refresh token stays in an HTTP-only cookie so frontend JavaScript cannot read it. Protected routes check the access token and fail through the same error path as a bad login.